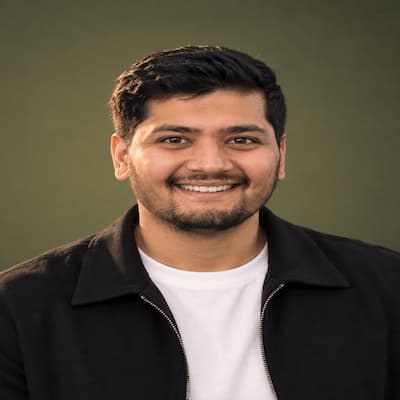
Dhairya Patel
Security Engineer with 3+ years across Security Operations (SOC), Incident Response and Detection Engineering. I currently work at Arctic Wolf, where I handle high-severity incident escalations, build detection logic mapped to MITRE ATT&CK, and run hypothesis-driven threat hunts across endpoint, network and cloud telemetry. Based in Waterloo, Ontario.
What I built
CVE Watch is a fully automated vulnerability-intelligence site. Every 6 hours it collects newly published CVEs, enriches them with exploitation data, publishes them here, and sends subscribers a daily email digest — with no server to run and zero hosting cost.
How it works
Collect
A scheduled GitHub Actions job queries the NIST NVD API 2.0 for every CVE published in the last 14 days, handling pagination and rate limits.
Enrich
Each CVE is cross-referenced with the CISA Known Exploited Vulnerabilities catalog and tagged with CVSS (v4 → v3.1 → v2), CWE and affected products.
Publish
The job commits a fresh dataset and redeploys this site on GitHub Pages. The page filters by severity, date, exploitation status and keyword in the browser.
Notify
An RSS feed of daily digests drives the email service, so subscribers get one email per day with critical/high CVEs and new KEV additions.
Why I built it
Defenders drown in volume
Well over a hundred CVEs are published on a typical day. In SOC and incident response work, the real question isn't "what's new" but "what do I act on first?" CVE Watch answers that by putting actively exploited and critical issues at the top.
Exploitation beats severity
A CVSS 9.8 nobody is exploiting can matter less than a 7.5 that's in CISA KEV and used by ransomware crews. Combining both signals mirrors how I prioritise during real incidents and threat hunts.
Automation is a security skill
Most of my biggest wins — a 32% MTTR reduction, a 40% drop in false positives — came from automating repetitive analyst work. This project applies the same mindset to vulnerability intelligence.
Built in the open
Everything runs on free, public infrastructure (GitHub Actions + Pages, public NVD and CISA data), so anyone can see exactly how it works and reuse it for their own team.
What I've done
Security Engineer — Arctic Wolf Networks
- Handle the incident response lifecycle from triage through containment and customer remediation guidance, with high-severity on-call escalations for financial, healthcare and SaaS customers.
- Reduced MTTR by 32% by redesigning alert-triage workflows, adding automated enrichment and speeding up L1/L2 → engineering handoffs.
- Build and tune SIEM correlation rules and EDR detection logic mapped to MITRE ATT&CK TTPs.
- Run hypothesis-driven threat hunts for low-and-slow intrusions, lateral movement and persistence.
- Delivered live exploit-development demos to 50+ security professionals to improve detection coverage.
Security Operations Center Engineer — Investis Digital
- Automated SIEM alert workflows and threat-detection logic, cutting manual triage time for the SOC team.
- Designed a WAF strategy aligned with OWASP Top 10, moving the environment toward ISO 27001 compliance.
- Cut false-positive volume by 40% through correlation-rule tuning and allowlist management.
Skills & tools
Detection & response
Offensive security
Frameworks
Identity, cloud & automation
Certifications
- CompTIA CySA+ (Cybersecurity Analyst+)
- CompTIA Security+
- Certified Ethical Hacker (CEH) v11
- Kali Linux Certified Professional (KLCP)
Education
- Post-Graduate Certificate, Offensive Cybersecurity — York University (2024)
- Post-Graduate Certificate, Cyber Security Operations — York University (2023)
- Bachelor of Computer Engineering — Gujarat Technological University (2021)
Let's talk
Happy to talk detection engineering, incident response, threat hunting or this project. The fastest way to reach me is LinkedIn or email.